Opening
HBO Max Reddit Account Compromised in Sophisticated Ad Fraud Attack
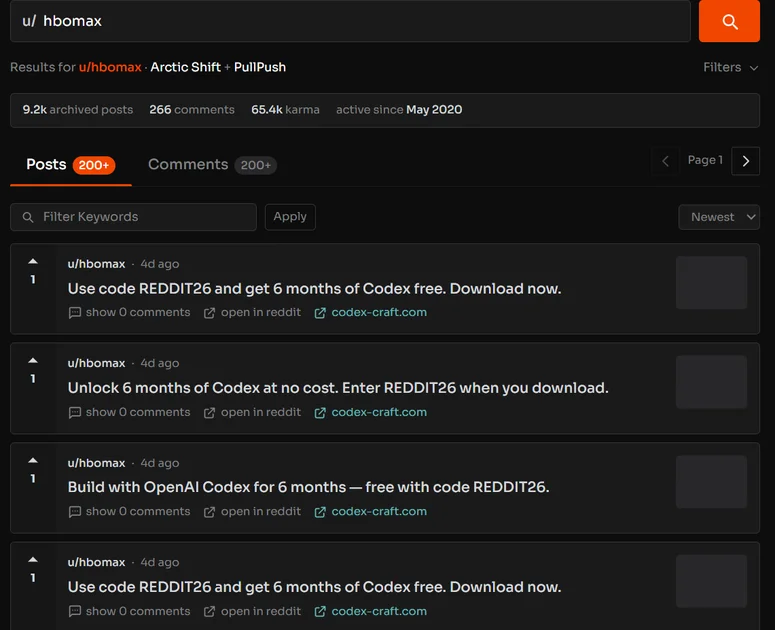
HBO Max’s official Reddit account was hijacked by a hacker group last week and used to run 108 different ad permutations targeting an unknown number of Redditors, according to a report from AdExchanger. The campaign, which ran for two days before being detected, promoted fake HBO Max downloads and promos through convincing landing pages hosted on “hbomax.us”—a domain designed to mimic the real “hbomax.com.”
The breach was discovered only when a cybersecurity professional in the r/cybersecurity subreddit was served one of the ads, blowing the scammers’ cover. Reddit subsequently locked the account and removed the ads, a spokesperson told AdExchanger. Warner Bros. Discovery, which owns HBO Max, did not respond to a request for comment.
According to Hudson Rock, the cybersecurity firm that analyzed the attack, the campaign was orchestrated by a sophisticated group with links to previously documented cyber and ad fraud operations. The compromised account was traced to someone working on the HBO Max team who fell victim to a credential-stealing scheme—likely a phishing page that mimicked a Google Ads login, leading the user to authorize a multifactor token for the attackers.
ClickFix Malware and Data Harvesting
The fake ads did not merely redirect users to fraudulent sites; they deployed a ClickFix lure, a tactic that tricks victims into copying and pasting a string of text into Windows Command Prompt or Mac Terminal. Executing the command installs info-stealing malware capable of harvesting passwords, access to logged-in accounts, and cryptocurrency wallets. Hudson Rock and ADAMnetworks noted that the ClickFix wave tied to this campaign involved hundreds of fake but authentic-looking Reddit ads.
Reddit said it has contained the account and taken down the ads, but it has not disclosed how many users were targeted or clicked. That silence leaves a critical question unanswered: was this a narrow burst of malicious ads or a wider compromise affecting far more users than acknowledged?
Context
Advertising Account Security: A Persistent Weak Link
The HBO Max incident is the latest in a string of account takeover scams plaguing major advertising platforms. These attacks exploit a simple reality: ad platforms are only as secure as their users. Fraudsters typically gain entry through human error—a search for “Google Ads account” that leads to a scam ad, a phishing email that mimics a legitimate login page, or a reused password.
Once inside, attackers can wreak havoc. In a separate but illustrative case reported earlier this week, a 9-year-old used his father’s logged-in Google business account to spend $118,000 on YouTube ads promoting a Minecraft and Roblox channel—despite a $20 spending limit. While that incident was benign, it highlights how easily ad accounts can be misused.
The stakes are higher when criminals are involved. Compromised ad accounts can be used to distribute malware, harvest personal data, and defraud advertisers. The HBO Max hack is particularly concerning because it leveraged a trusted brand’s verified account, lending false legitimacy to malicious ads.
The Rising Cost of Privacy and Fraud Litigation
The ad tech industry is also facing mounting legal pressure. According to a new report from the International Association of Privacy Professionals (IAPP), more than 10,000 data privacy cases have been filed in US courts since 2022, with 3,414 in 2025 alone. Settlements have reached roughly $7 billion. Plaintiff attorneys are creatively applying decades-old statutes—such as the Video Privacy Protection Act of 1988 and the California Invasion of Privacy Act of 1967—to modern tracking technologies like pixels and web beacons.
Müge Fazlioglu, a principal researcher at IAPP, told AdExchanger that privacy litigation is “no longer a minor risk” but “a major source of legal and financial exposure.” While the HBO Max case is not a privacy lawsuit, it underscores the broader vulnerability of digital advertising ecosystems, where account takeovers can lead to data breaches and regulatory scrutiny.
Perspective
What the HBO Max Hack Reveals About Platform Security
The incident raises uncomfortable questions for platforms like Reddit, Google, and their advertisers. Reddit’s response—locking the account and removing ads—was reactive, not proactive. The two-day window during which malicious ads ran unchecked suggests that automated fraud detection systems may not be sufficient to catch compromised accounts in real time.
For advertisers, the lesson is clear: account security is not just an IT issue but a business risk. Multifactor authentication, regular audits, and employee training are essential, yet human error remains a persistent threat. As ad fraudsters grow more sophisticated, platforms may need to invest in behavioral analysis and anomaly detection to flag suspicious account activity before damage is done.
Meanwhile, the advertising industry continues to grapple with structural challenges. In a separate antitrust ruling unsealed last week, Google was ordered to make significant changes to its ad tech business, including sharing bid data with publishers and submitting AdX bids to rival ad servers on equal terms. A court-appointed technical monitor will oversee compliance globally. While the remedies aim to restore competition, they also introduce new complexities for an ecosystem already struggling with fraud and privacy concerns.
For now, the HBO Max Reddit hack serves as a reminder that even verified, trusted accounts can be turned into weapons. As Reddit has yet to disclose the full scope of the breach, users and advertisers alike are left wondering: how many other compromised accounts are lurking, waiting to be activated?
Comments